Provisioning a Load Balancer
Sign in during Public Preview to get the Team plan free, plus an early-adopter discount when we launch. Sign in
Provisioning a Load Balancer
This guide shows you how to provision a Load Balancer against Locally. As with the other guides we're going to use the Azure CLI, but the same resources can be provisioned with HashiCorp Terraform, Pulumi or Bicep too.
Before you start
- The Azure CLI (
az) installed. - Locally installed, with Locally Setup completed.
1. Start Locally
Firstly, we need to launch Locally which we can do from a terminal by running:
                $


            locally build
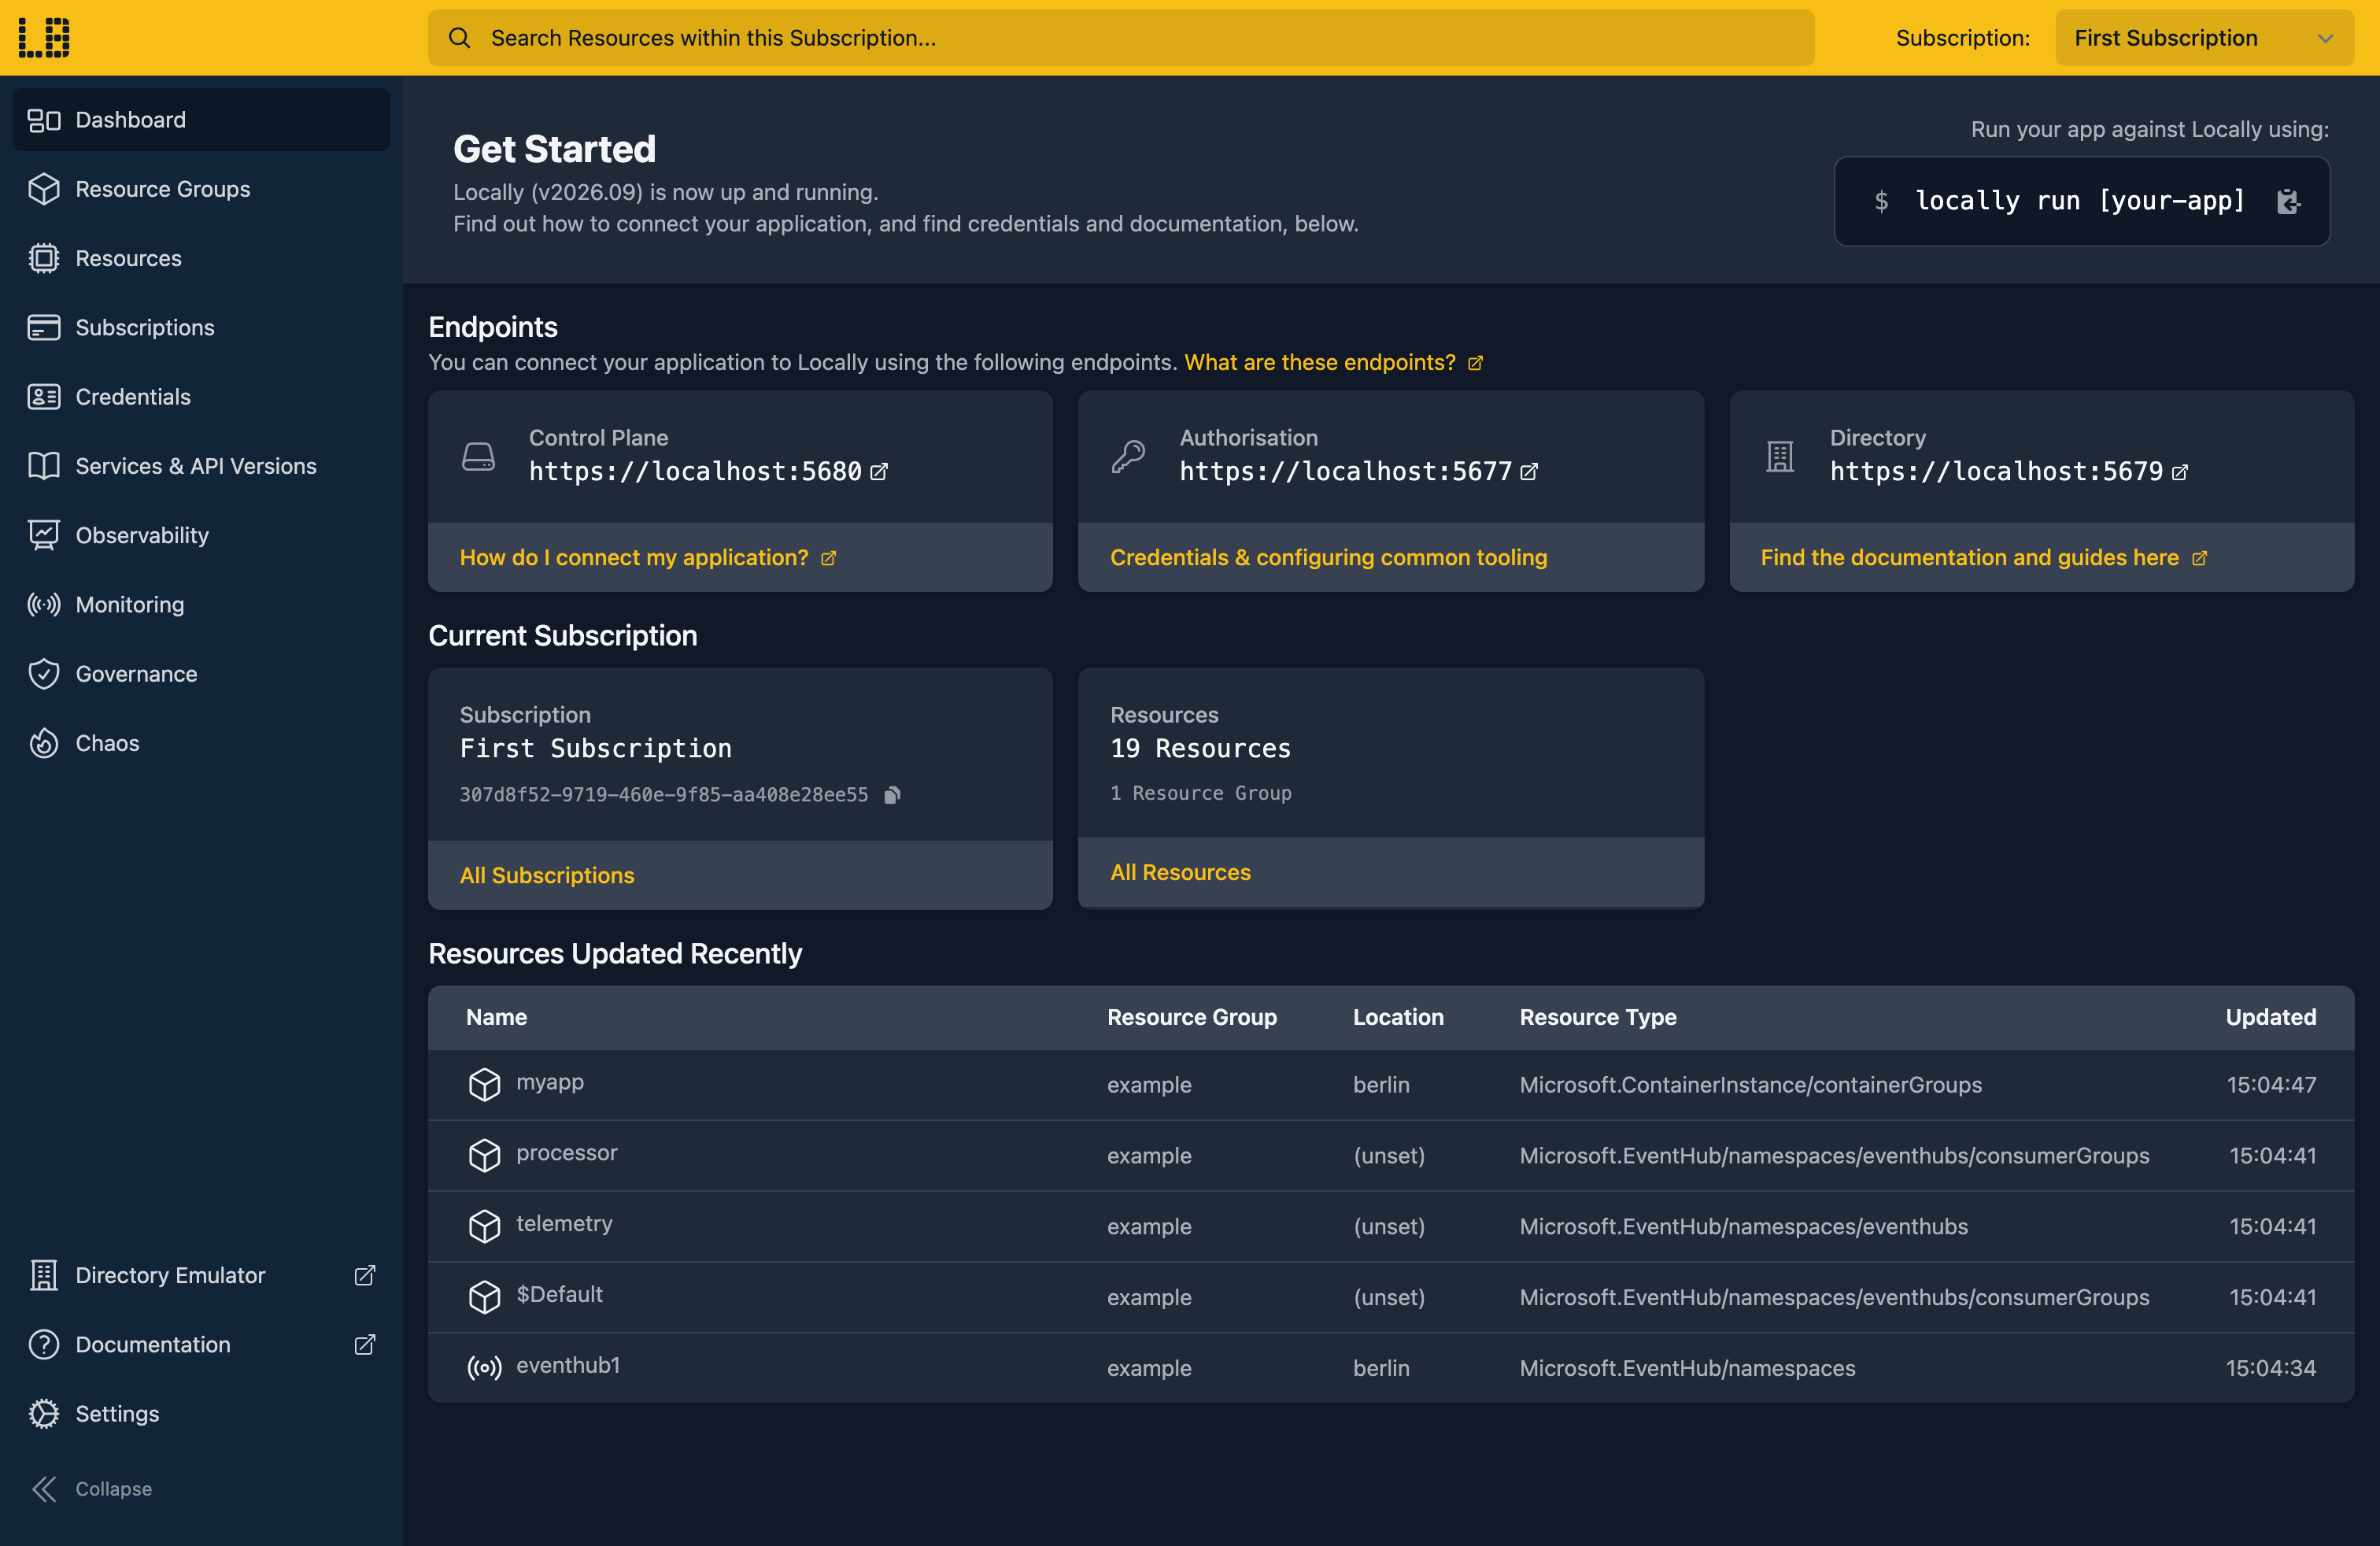
Once Locally has started, the Locally Dashboard will open automatically:
2. Create a Resource Group
Next we can create the Resource Group:
                $


            locally run az group create -n sample-resources -l berlin
There's two things to note here:
- The Azure CLI supports Automatic Configuration, meaning that it can automatically be configured to work against Locally just by prefixing commands with
locally run. - Locally intentionally uses a different set of locations to Azure as a safety precaution, so that you can be confident you're deploying against Locally rather than regular Azure. You can also configure Locally to use the Azure locations too, but you'll want to be extra sure that you're prefixing commands with
locally runwhen you do.
3. Create a Public IP Address and the Load Balancer
A load balancer needs somewhere to receive traffic, so we'll create a Public IP Address for its frontend first:
                $


            locally run az network public-ip create -g sample-resources -n sample-pip --sku Standard --allocation-method Static
Then the load balancer itself, wiring that address to a frontend configuration and creating an empty backend pool:
                $


            locally run az network lb create -g sample-resources -n sample-lb --sku Standard --public-ip-address sample-pip --frontend-ip-name frontend --backend-pool-name backend
We can read it back to see what was created:
                $


            locally run az network lb show -g sample-resources -n sample-lb --query "{name:name, sku:sku.name, frontend:frontendIPConfigurations[].name, backend:backendAddressPools[].name}"
{
  "backend": [
    "backend"
  ],
  "frontend": [
    "frontend"
  ],
  "name": "sample-lb",
  "sku": "Standard"
}
4. Add a health probe and rule
A load balancer with no health probe has no way of knowing whether a backend is healthy, so that's next:
                $


            locally run az network lb probe create -g sample-resources --lb-name sample-lb -n health --protocol Tcp --port 80
{
  "name": "health",
  "port": 80,
  "protocol": "Tcp"
}
Then a rule tying the frontend, the backend pool and the probe together - this is what actually forwards traffic:
                $


            locally run az network lb rule create -g sample-resources --lb-name sample-lb -n http --protocol Tcp --frontend-port 80 --backend-port 80 --frontend-ip-name frontend --backend-pool-name backend --probe-name health
{
  "backendPort": 80,
  "frontendPort": 80,
  "name": "http",
  "protocol": "Tcp"
}
Note
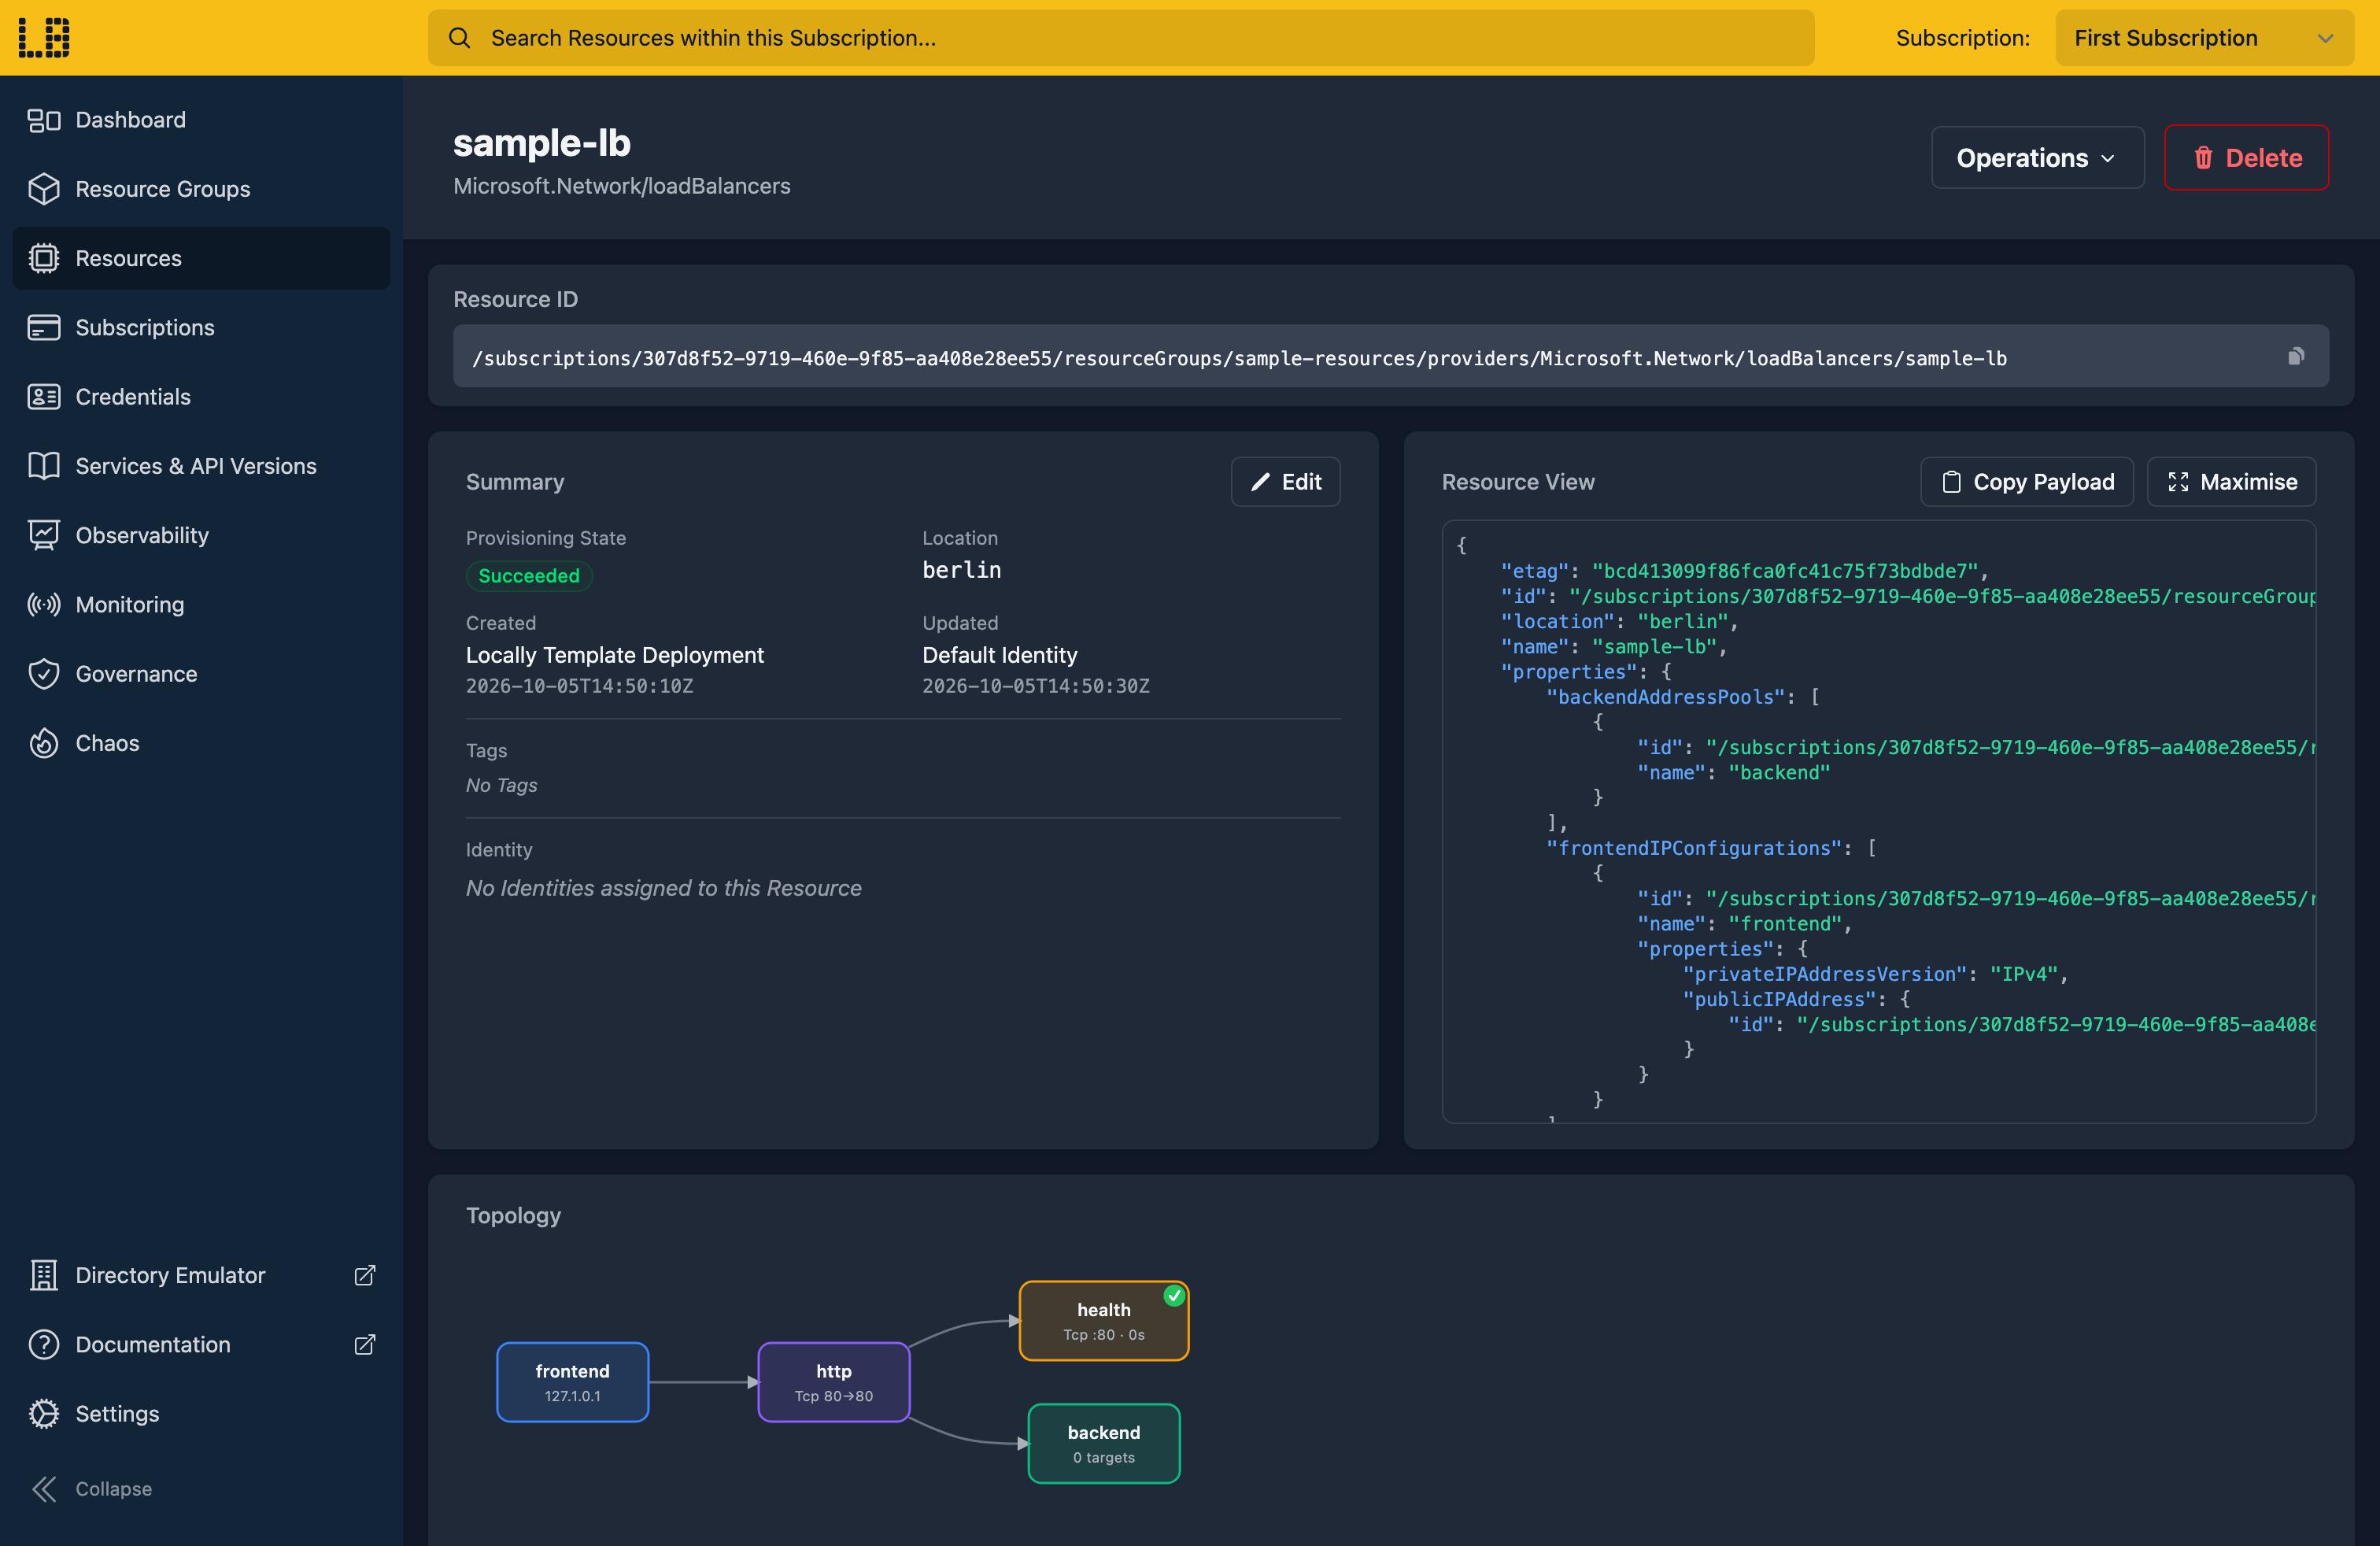
We can see the Load Balancer in the Locally Dashboard too:
5. Tidy up
Finally, we can tidy up. To remove the Resource Group and everything within it:
                $


            locally run az group delete -n sample-resources --yes
There's nothing billable to clean up, since everything ran on your machine, but it's still worth checking your teardown scripts work here before you run them against Azure.
Doing this with other tooling
Whilst this guide used the Azure CLI, Load Balancers work the same way through any of the tooling that Locally supports - a Microsoft.Network/loadBalancers resource in HashiCorp Terraform or OpenTofu, Pulumi, Bicep or an ARM Template all provision against Locally in the same way, with only the location changed.
Next steps
For outbound traffic from a subnet, see NAT Gateway.
Should you encounter any issues, please take a look at the troubleshooting section.
Sign in during Public Preview to get the Team plan free, plus an early-adopter discount when we launch. Sign in
